Book a call

Every release,on the record.

CRA evidence for every release, prepared for you.

SBOMs, exploited-vulnerability checks, VEX and ENISA report drafts for device makers with 10 to 249 staff. Your team reviews and signs.

Taking our first founding clients. Or email chhabi@relvault.com

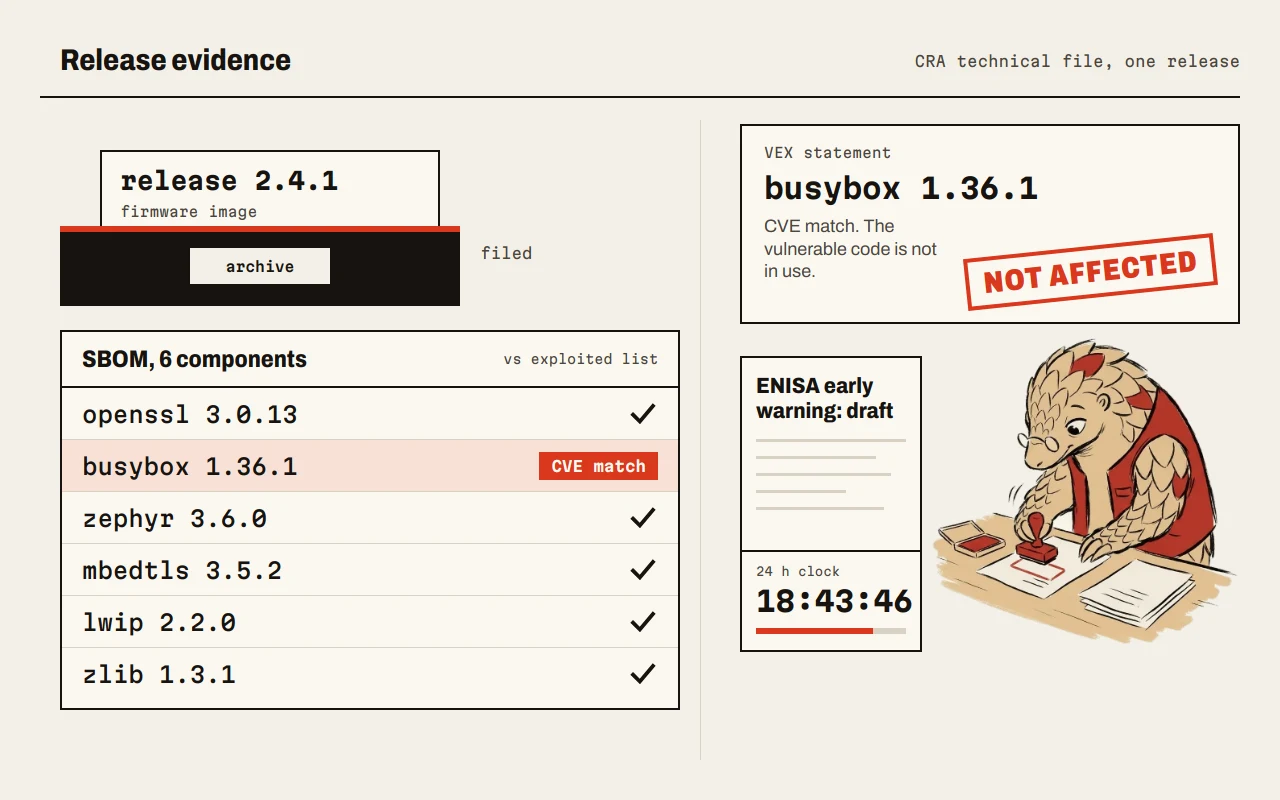
A short film. A firmware release slides into the vault, and Kavach checks it and stamps the record.
Kavach the pangolin stands next to an open filing cabinet full of records. It holds a clipboard and smiles at you.

The clock started on 11 September.

Since 11 September 2026, the reporting duties of Article 14 apply. They also cover products that are already on the market.

Kavach holds up a red stopwatch and looks at it with care.

11 Sep 2026

Reporting applies

Source: Art. 71, Regulation (EU) 2024/2847

10 Dec 2024

The CRA entered into force

Source: Art. 71, Regulation (EU) 2024/2847

On the market

Products already on the market are covered

Source: Art. 69(3), Regulation (EU) 2024/2847

Article 14 reporting clocks

Reporting applies 11 Sep 2026

An actively exploited vulnerability

The clock starts when you become aware of it.

  1. 24h
    Early warning

    Within 24 hours of becoming aware.

  2. 72h
    Notification

    Within 72 hours, with the details you know.

  3. 14days
    Final report

    No later than 14 days after a fix or mitigation is available.

A severe incident

Same first two steps. The last one is slower.

  1. 24h
    Early warning

    Within 24 hours of becoming aware.

  2. 72h
    Notification

    Within 72 hours.

  3. 1month
    Final report

    Within one month after the notification.

You decide whether to report, and you file each report. We prepare the drafts.

Three terms, in pictures.

Kavach pulls a very long paper list out of a small device box.

SBOM

A parts list for your software.

An SBOM lists the software components in a release, with their versions. The CRA asks for at least the top-level dependencies; we list every component we can find. Customers and authorities can ask for it. We build one for each version.
Kavach pins small posters with bug pictures on a board.

Exploited vulnerability

A flaw that attackers already use.

CISA keeps a public list of such flaws. If a flaw on the list is in your product and you become aware of it, the 24-hour clock starts. With maintenance, we check your SBOMs against the list every day.

Kavach presses a red stamp onto a sheet of paper on a low table.

VEX

A note that says if a flaw really affects you.

A match on a list does not mean your product is affected. A VEX statement gives the status and the reason. Kavach stamps "not affected" only after your engineer agrees.

Everything your customer asks for, in one place.

For each product family, we prepare the documents that your customers and the authorities can ask for. Each one is filed in your own repository.

No. RV-01

An SBOM for every version

A software bill of materials in CycloneDX for each product version, with a note on gaps. SPDX on request.

  • One file for each product version
  • Scored for completeness, with a gap note
  • An open format, so you can read it without us
No. RV-02

A daily exploited-vulnerability check

Every day, we check each SBOM against CISA KEV, the EU Vulnerability Database (EUVD) and OSV.

With maintenance
No. RV-03

VEX drafts

A draft for each match, with the reason. Your engineer confirms each "not affected" status.

No. RV-04

ENISA report drafts

Prefilled templates for the 24-hour early warning, the 72-hour notification and the final report. You file them.

No. RV-05

A technical-file index

What exists, where it lives, and a list of gaps with owners. With draft policies for disclosure, security contact and support period.

No. RV-06

Customer questionnaire answers

Answers to the CRA questionnaires that your customers send, based on the evidence. You sign and send them.

Four steps. You keep the pen.

We do the preparation. Your engineers check it, and your company signs and files.

2 to 3 weeks

To set up one product family

Our aim, not a promise.

4 to 6 hours

Your team's time

An estimate for the whole setup.

What we need from you

  • Your product list, with the versions you support.
  • Build files, or read-only access to your build.
  • One technical contact, for a few short reviews.

Today we do this by hand, with established open-source tools. We automate the repeated steps as we go.

Kavach reads a questionnaire on a clipboard and thinks.
  1. Intake call

    We talk about your products and what your customers ask for. We sign an NDA and a data processing agreement before we see any data.

  2. SBOM and inventory

    We list products, versions and support periods. We build an SBOM for each version, from your build or from build files that you send.

  3. Daily watch and drafts

    We check the SBOMs against exploited-vulnerability lists. We draft VEX, ENISA reports, policies and questionnaire answers.

  4. You review, sign, file

    Your engineers confirm each VEX status. You sign the documents and file each report.

Meet Relvault.

The reporting clock, the evidence it asks for, and how we prepare that evidence for you, in 85 seconds.

With voice and English captions. The video loads only when you press play.

Your code stays home.

We hold as little as possible, for as short a time as possible. This is what we promise.

Your repository first.

Your code stays in your own repository where possible. Our access is read-only, and you can remove it at any time.

Kavach curls around a small locked drawer box to protect it.

Paper before data.

We sign an NDA and a data processing agreement before we see any data.

A dedicated, encrypted Relvault device.

Working copies live only on a device that is used for Relvault and nothing else, with full-disk encryption. Never an employer's computer. Never a shared one.

Only what we need.

We ask for the data the work needs, and no more.

No AI tools on your data.

Not without your written consent.

Two-step login everywhere.

On every account that touches your work.

Deleted when the contract ends.

We confirm the deletion to you in writing.

24 h

If something goes wrong, you hear from us within 24 hours.

Two prices. Nothing hidden.

A product family is up to 3 related products on one code base.

Setup: you pay 50% at signing and 50% on delivery. Maintenance: invoiced monthly in advance. All prices exclude VAT.

Kavach holds out a long paper receipt toward you with one paw and nods politely.

Setup

No. S-01

€2,500

per product family, one time

  • An SBOM for each product version
  • An exploited-vulnerability report and VEX drafts
  • Draft policies for vulnerability handling
  • ENISA report templates, prefilled
  • A technical-file index with a gap list
  • Answers to the questionnaire that started the project
  • A 60-minute handover

Maintenance

No. M-01

€450

a month, per product family

  • A daily check against CISA KEV, EUVD and OSV
  • Review of up to 2 releases a month, with VEX updates
  • Up to 2 questionnaire or tender answers a month
  • A monthly evidence report
  • A quarterly review of support periods and policies
  • Up to 3 hours of incident support a month

€1,500 setup and a 12-month price lock.

Relvault is new. The first 3 to 5 clients pay €1,500 for setup instead of €2,500. Their monthly price stays the same for 12 months. In return, we ask for honest feedback and, if you are satisfied, a short testimonial.

What we will never do.

We prepare technical evidence. Legal and conformity decisions stay with you and your advisers.

  • Give legal advice.
  • Certify a product or decide conformity.
  • Say that your product meets the CRA. Only your own assessment decides that and, where the law requires it, a notified body.
  • File a report for you.
  • Run penetration tests or write EN 18031 test reports.
  • Promise that we catch every vulnerability. Lists can be late and SBOMs can have gaps. We write every gap down.

One engineer. Every item checked by hand.

Relvault is run by one software engineer, based in Nepal, who works with clients remotely, in English.

Relvault is new and small. When this site says "we", it means that one engineer. You would be one of the first 3 to 5 clients.

Nepal is 3 h 45 min to 4 h 45 min ahead of Central European Time, so calls fit the European afternoon. The GDPR applies to our work in full.

engineer

Based in Nepal. Works remotely, in English.

Questions buyers ask us.

Not here? Ask us at chhabi@relvault.com.

Kavach rolled up into a ball of layered scales.
Do you certify our products?

No. We prepare evidence. We do not certify products or decide conformity, and we never say that a product meets the CRA. You sign the EU declaration of conformity. Where the CRA requires it, a notified body assesses the product.

Is this legal advice?

No. We do not interpret the law for your case, for example the scope or the product class. When a question needs a lawyer, a test lab or a CRA consultancy, we tell you.

Do you need access to our code?

Not always. We can set up open-source SBOM tools in your build pipeline together with your engineers, or run them on build files that you send. We do not ask for long-lived access to your systems. Any access we use is read-only, and you can remove it.

Where is my data?

By default, the evidence stays in your own repository. We keep working copies only while the work needs them, encrypted on a dedicated Relvault device in Nepal, and we delete them when the contract ends. We sign an NDA and a data processing agreement before we see any data. We do not put your data into third-party AI tools without your written consent.

We already have an SBOM tool. Is this still useful?

Yes, if the work around the SBOM takes your engineers' time. We use your SBOMs as they are and add the rest: the exploited-vulnerability check, VEX drafts, ENISA report drafts, the technical-file index and questionnaire answers.

Can you file the ENISA report for us?

No. You file it. We prepare the draft and the runbook, so the 24 hours go into the decision and not into the paperwork.

What happens if you stop?

You keep everything. The evidence is in your repository, in open formats (CycloneDX and CSAF). The tools are open source, so your engineers can keep running them. At the end, we hand over a short runbook.

Do your customers already ask CRA questions?

Send a short email. Tell us what your product is and what your customers ask for.

Book a call